How we keep production systems safe
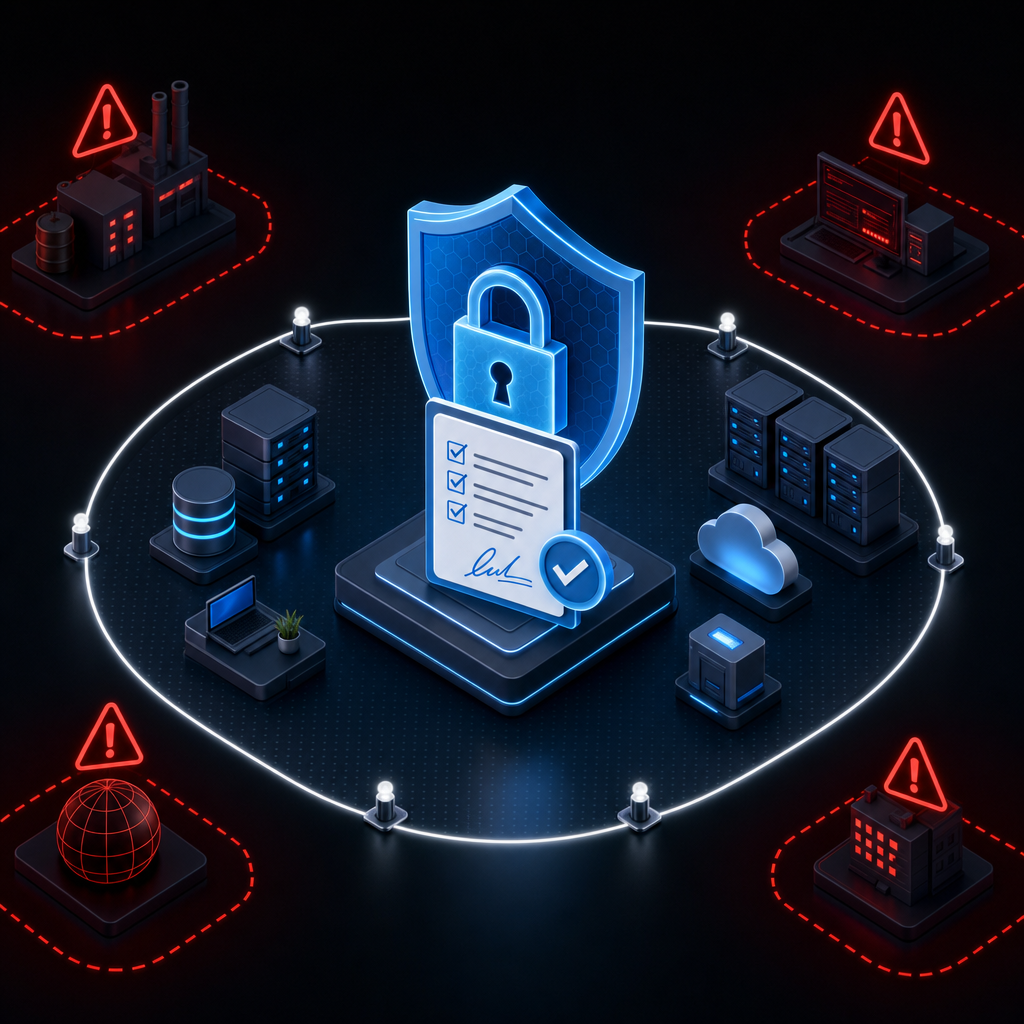
✓Fully scoped & pre-authorized before any testing begins
✓Configurable maintenance windows & rate limiting
✓Full audit trail of every action taken
✓Explicit exclusion lists for sensitive/critical systems
✓Human expert review before any high-impact exploit is attempted
✓Signed authorization agreement required for every engagement