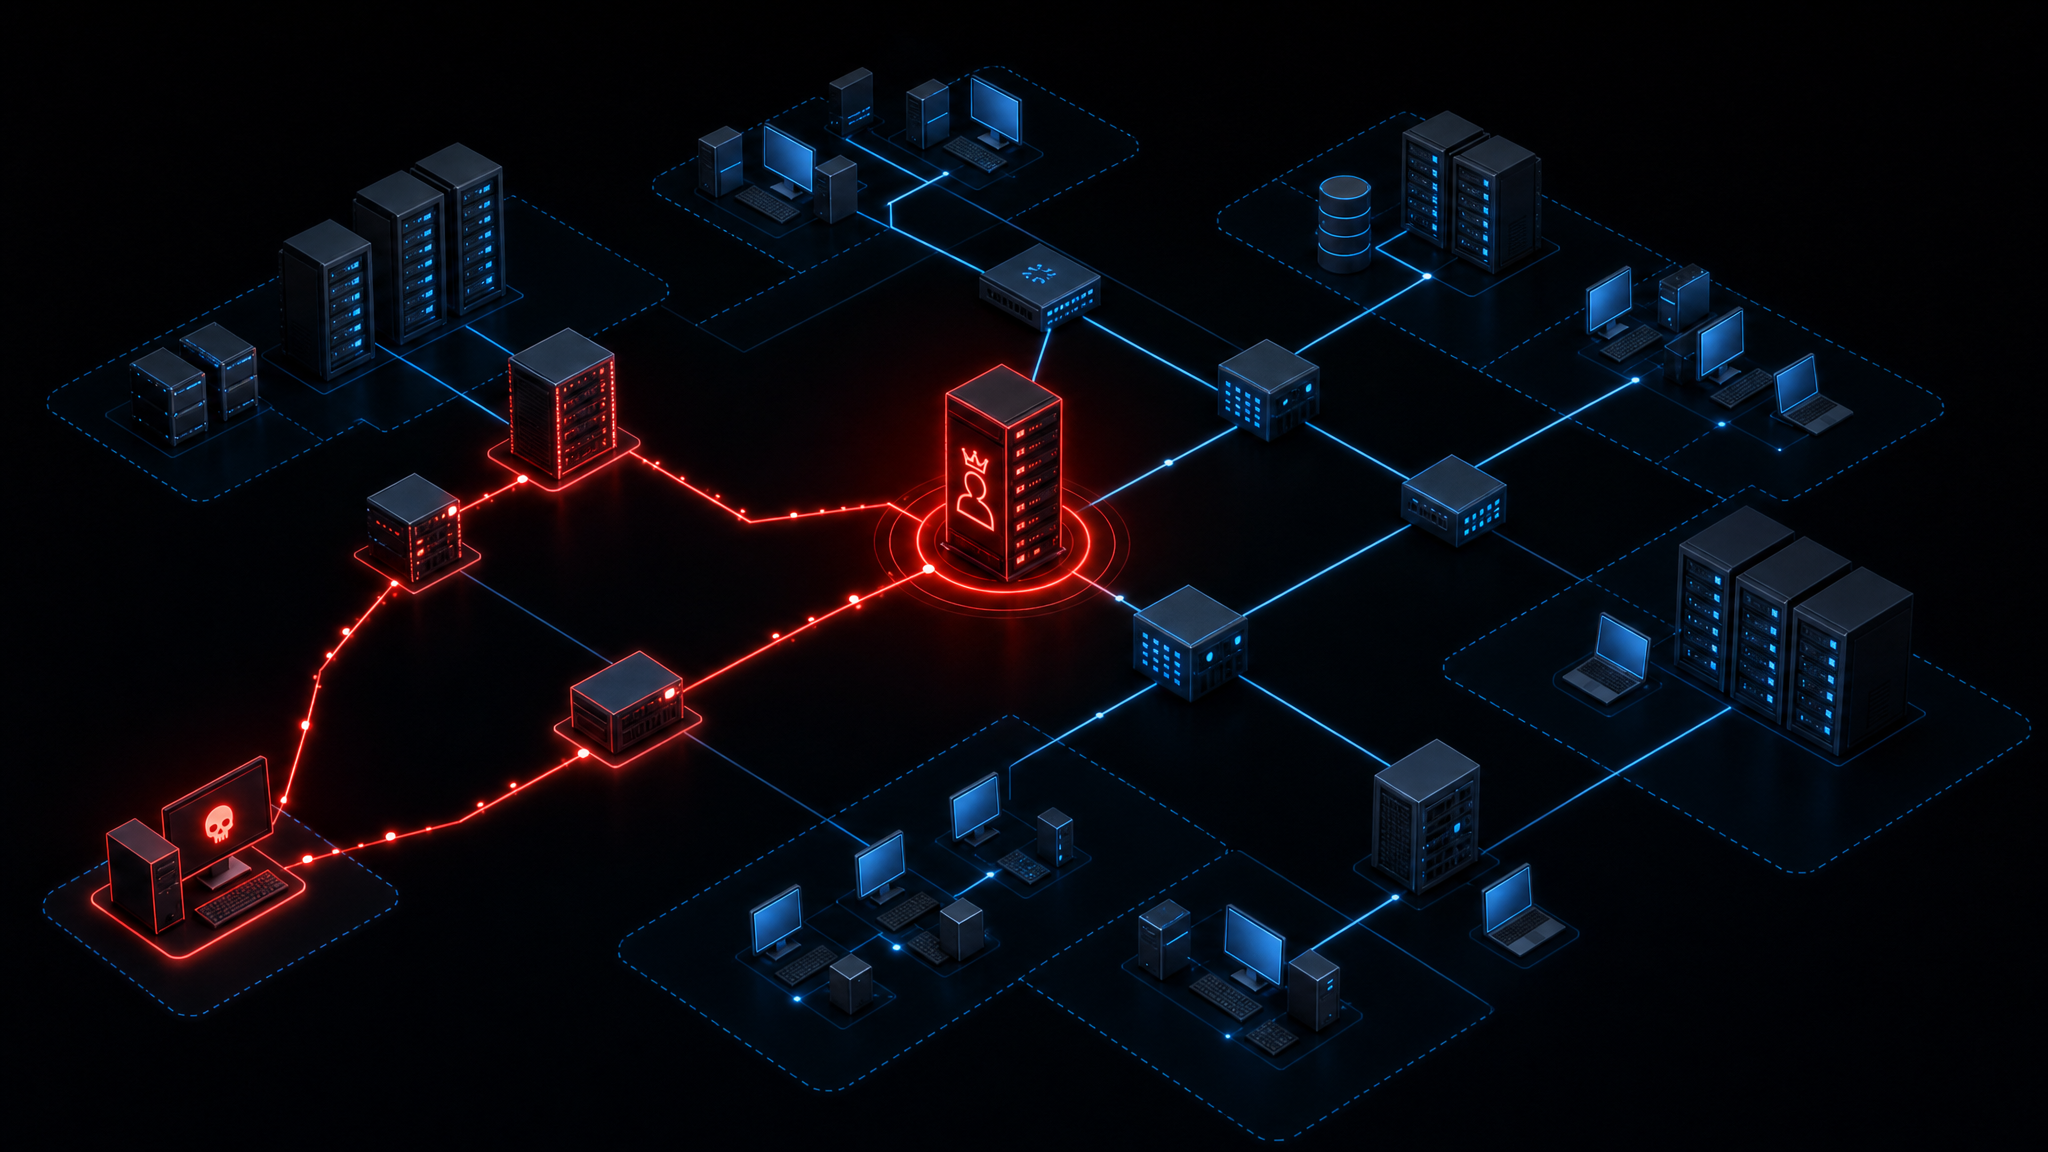
Controlled, scoped, fully authorized exploitation — not a vulnerability scan with a fancy name.
Cached logon exposure, password reuse detection, offline hash cracking against captured credentials.
Full domain mapping — trust relationships, group memberships, Kerberoastable service accounts, delegation misconfigurations.
Identifying and exploiting local + domain-level paths from standard user to Domain Admin.
Simulated movement across the network using real attacker tradecraft — pass-the-hash, token impersonation, SMB relay.
Identifying hosts vulnerable to relay attacks due to disabled signing — a top real-world breach vector.
Both your public-facing attack surface and your internal network are in scope, based on the engagement plan.
Every Red Team engagement runs inside a signed authorization agreement, with exclusion lists for sensitive systems, configurable maintenance windows, and a full audit trail of every action taken. Nothing runs against production systems without pre-approval.
Every Red Team finding feeds directly into our Blue Team remediation process — and then gets re-tested by Purple Team to confirm the fix worked.