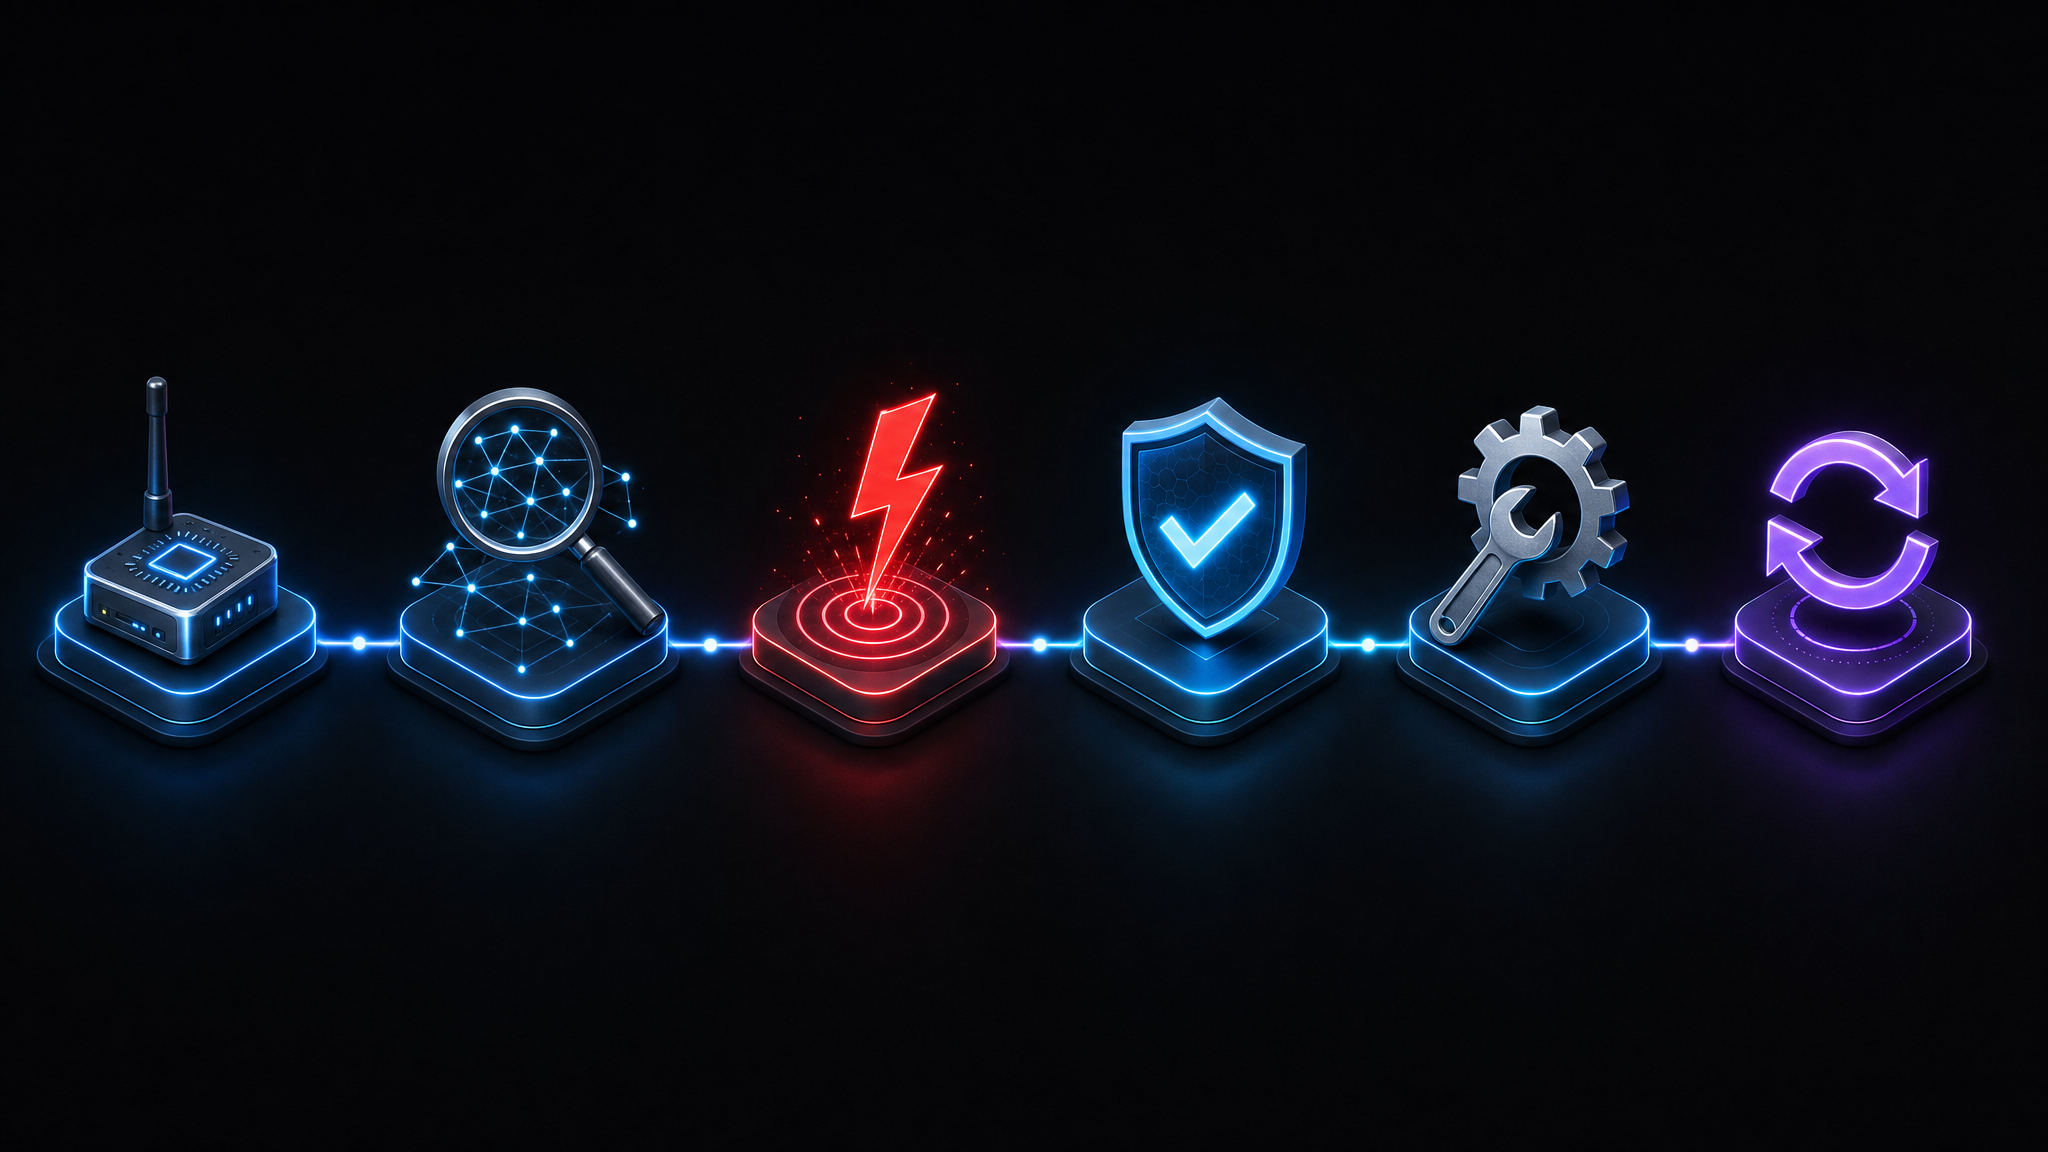
01 · Deploy
Lightweight agent or appliance deployed to your network, no infrastructure changes required. Onboarding is guided by our team.
02 · Discover
We map the full attack surface — hosts, services, trust relationships, exposed credentials — before any exploitation begins.
03 · Attack
Controlled, scoped exploitation inside your signed authorization agreement — AD attacks, credential capture, lateral movement, privilege escalation.
04 · Validate
We confirm real compromise paths exist — not just theoretical CVSS scores that may not reflect actual exploitability in your environment.
05 · Remediate
Prioritized, actionable hardening guidance delivered directly to your team — see Blue Team for detail.
06 · Re-Test
Automatic re-validation confirms the fix actually closed the gap — see Purple Team for detail.